OAuth 2.0 authentication type
OAuth 2.0 authentication type is used when the service provider requires client credentials like Client ID and Client Secret.
Create a connection for the OAuth 2.0 authentication type
To make HTTP(S) requests that require an OAuth 2.0 authorization, you must create an OAuth connection first. For that, you need:
- An app/service account
- Access to a developer portal or settings
- A Redirect URI (sometimes called a Callback URL)
- App/service credentials
Obtain credentials in the app
Create an OAuth client in the app that you want to connect with Make. To do this, enter the developer portal or settings.
- Specify a Redirect URI: https://www.integromat.com/oauth/cb/oauth2.
- Obtain client credentials. Those are usually called Client ID and Client Secret, but can also be defined as App Key and App Secret, or another way.
- Save the client credentials in a safe place. You will need them when building a scenario in Make.
Find the Authorize URI and Token URI in the app's API documentation. These are the addresses through which Make communicates with the app.
Create a connection in Make
Once you've got the required credentials from the app, you can select OAuth 2.0 as an authentication type in the HTTP > Make a request module, click Create connection, and fill in the required fields:
Field | Description |
|---|---|
Connection name | Enter the name for your connection. |
Flow type | Select the flow:
|
Scopes | Add API scopes. Refer to the service's API documentation to find the required scopes. |
Client ID | Enter the credentials you saved from your app/service. |
Client Secret | Enter the credentials you saved from your app/service. |
In the Advanced settings, you can also configure:
Field | Description |
|---|---|
Scope separator | Select scope separator: COMMA or SPACE. SPACE is the standard separator. When multiple scopes are requested in a URL query parameter, the space is URL-encoded as %20 or +, e.g., scope=read%20write%20profile. COMMA is a common non-standard separator. Some service providers accept or even require this separator in the request, e.g., scope=read,write,profile |
Authorize parameters | If needed, enter additional authorization request parameters as a key-value pair. |
Access token parameters | If needed, enter additional access token request parameters as key-value pairs. |
Refresh token parameters | If needed, enter additional refresh token request parameters as key-value pairs. |
ACCESS TOKEN SETUP | |
Custom Headers | Specify any custom headers to send in the request. |
Access token placement | Select whether to send the token in the header, query parameters, or both. |
Token name | Enter the name of the authorization token in the header. The default value is Bearer. |
You can edit the connection at any moment in the Connections section. For that:
- Click Connections in the left sidebar.
- Click three dots > Edit next to the required OAuth connection.
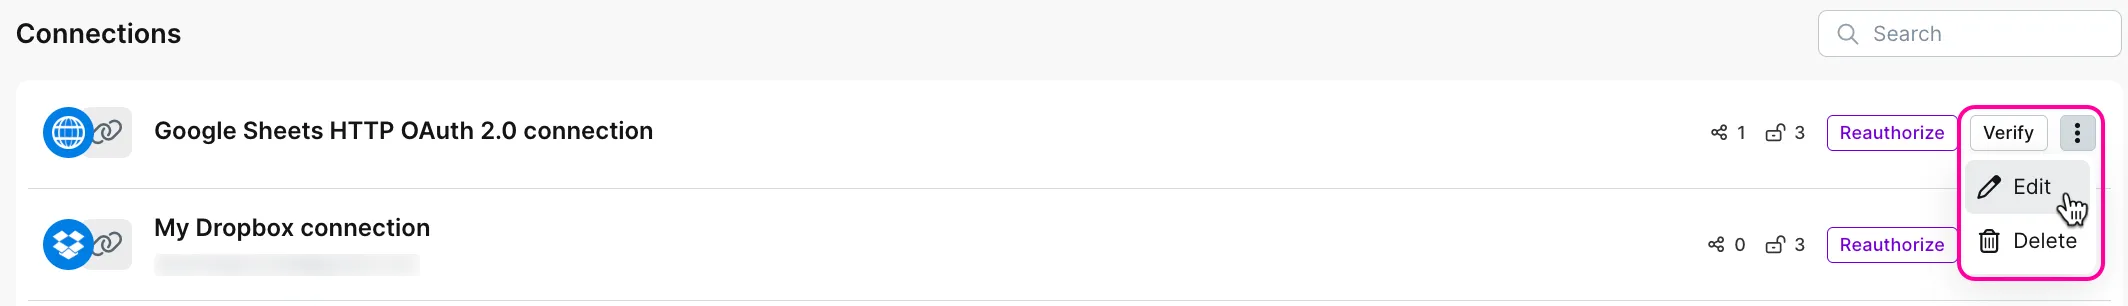
You will see the Edit window. Add or remove scopes, edit available authentication parameters, and click Save. All the modules that use this connection will be automatically adjusted.